Compliance Solutions for B2B SaaS Companies
As your B2B SaaS business scales, maintaining compliance with global standards like ISO 27001, SOC2, and GDPR is critical. We provide tailored compliance to ensure you stay secure, scalable, and fully compliant.
Learn MoreKey compliance challenges
B2B SaaS companies face several compliance hurdles, including the need to protect sensitive customer data, adhere to data privacy regulations, and ensure scalability while maintaining the security requirements of clients and partners. Some of the most common challenges include:
Limited Bandwidth
Limited internal resources - both in time and personnel - handling security and compliance can feel unsustainable.
Navigating Unfamiliar Territory
Working to meet audited frameworks without first hand experience can feel like stepping into a complex landscape without a clear map.
Delays Derail Progress
Mistakes and bottlenecks in meeting requirements can jeopardize timelines and risk costly setbacks.
How Athenisec Is Different
We handle the work rather than hand you a checklist, and we do it without tying you to any one vendor.
See how we’ve helped companies achieve and maintain compliance.
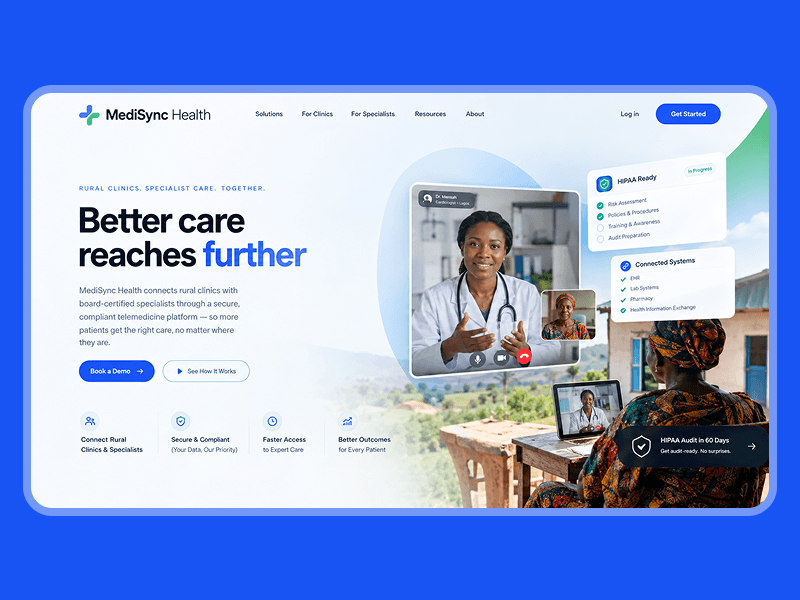
MediSync Health
Telemedicine SaaS platform connecting rural clinics with specialist doctors. 45-person team, $2.3M ARR.
- HIPAA
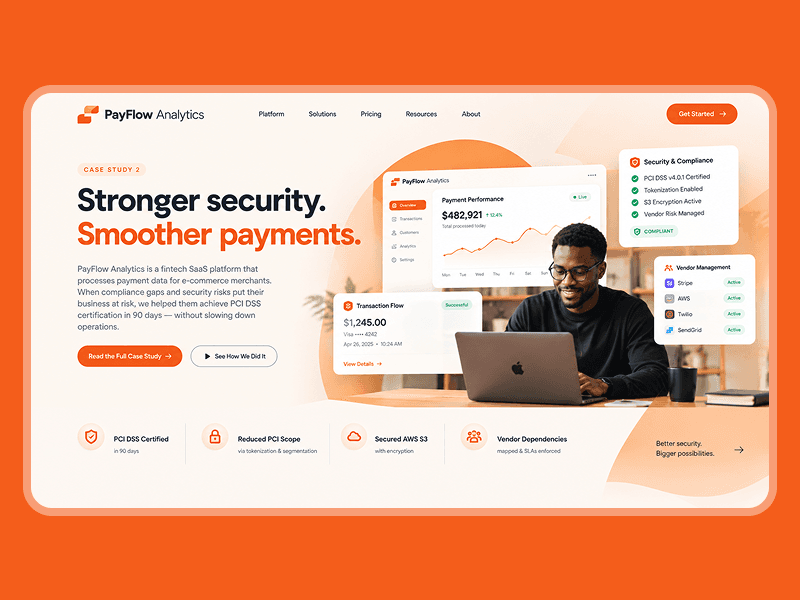
PayFlow Analytics
Fintech SaaS processing payment data for e-commerce merchants. 30-person team, $1.8M ARR.
- PCI DSS
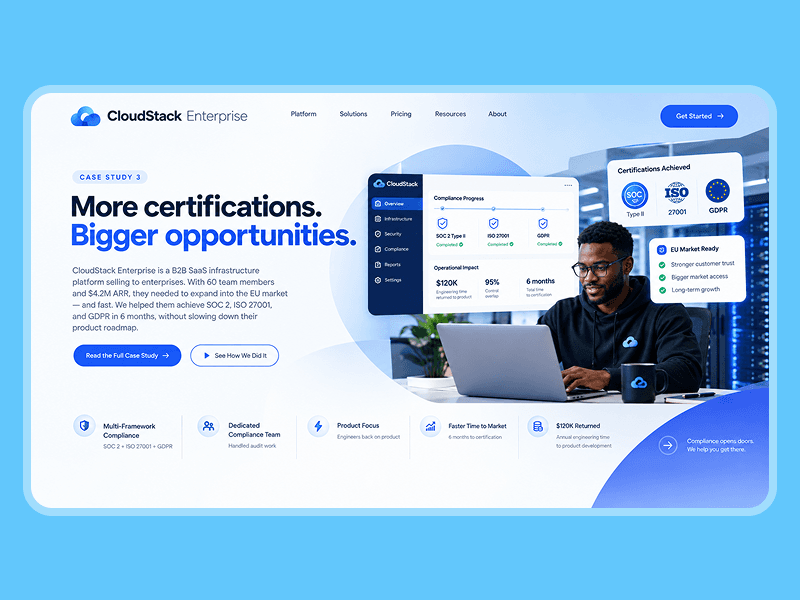
CloudStack Enterprise
B2B SaaS infrastructure platform selling to enterprises. 60-person team, $4.2M ARR.
- SOC 2
- ISO 27001
- GDPR