Achieve & Maintain SOC 2 with Unmatched Ease
Your dedicated team takes care of your entire SOC2 process from start to finish with uncompromising quality and speed.
Get StartedCertification Process Details
Planning
SOC 2 Type II audits evaluate your systems and processes against the Trust Service Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Most importantly, not all SOC2 reports are the same – they reflect the unique controls that you decide apply to your organization and your clients. Athenisec works with hundreds of clients to define audit scopes tailored to the needs of their specific clients.
Audit Preparation
SOC 2 Type II audits assess how well your controls operate over a defined period, typically 3-12 months. During this time, you'll need to demonstrate consistent adherence to the controls and policies you've implemented. Athenisec handles all of the implementation for you, from configuring logging to managing employee compliance and creating documentation.
Evidence Gathering
Throughout the audit period, your auditor will request documentation that proves your controls are functioning as intended. This includes logs, reports, and records of activities such as access controls, incident responses, and system monitoring. Athenisec gathers and prepares all of this evidence, so your team doesn't need to lift a finger.
The Audit
A certified third-party auditor conducts the SOC 2 Type II audit. The process involves reviewing your evidence, testing the effectiveness of your controls, and validating that your operations align with SOC 2 standards throughout the defined period.
Receive the Audit Report
At the end of the audit, the auditor provides a detailed report. This document outlines the controls evaluated, the tests performed, and the results, including any findings. A clean report demonstrates your commitment to protecting customer data and adhering to industry standards.
Ongoing Maintenance
SOC 2 Type II compliance requires annual audits to maintain certification. In your initial assessment, you define what your organization will do, and then you need to do those things with no exceptions. Continuous monitoring and process improvements ensure your systems stay secure and ready for future reviews, making the renewal process smoother. Athenisec manages this process for you, ensuring that future audits are as smooth as your first.
Highlights of SOC 2 Compliance
The controls we implement and monitor throughout your SOC 2 engagement.
See how we’ve helped companies achieve and maintain compliance.
MediSync Health
Telemedicine SaaS platform connecting rural clinics with specialist doctors. 45-person team, $2.3M ARR.
- HIPAA
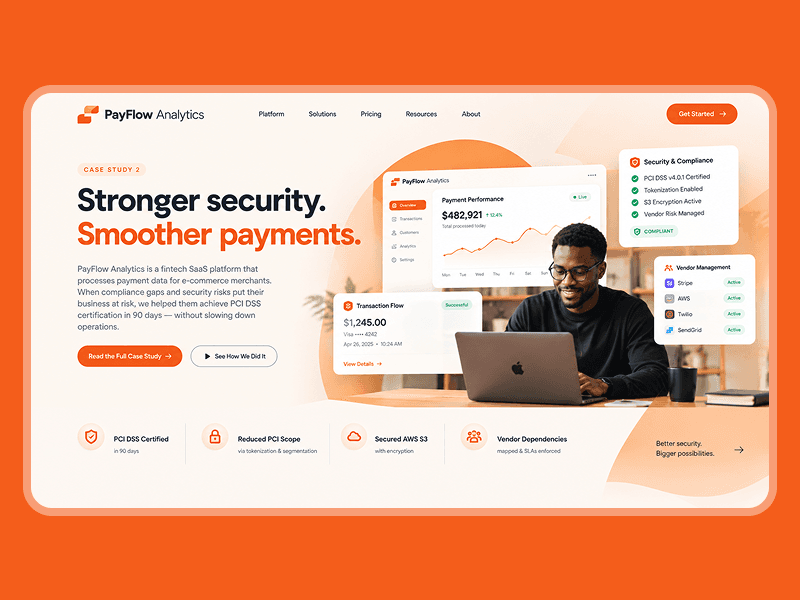
PayFlow Analytics
Fintech SaaS processing payment data for e-commerce merchants. 30-person team, $1.8M ARR.
- PCI DSS
CloudStack Enterprise
B2B SaaS infrastructure platform selling to enterprises. 60-person team, $4.2M ARR.
- SOC 2
- ISO 27001
- GDPR