Achieve & Maintain PCI DSS with Unmatched Ease
Your dedicated team takes care of your entire PCI DSS process from start to finish with uncompromising quality and speed.
Get StartedCertification Process Details
Planning
The newly released PCI DSS 4.0 includes 12 core requirements focusing on areas like encryption, access control, monitoring, and vulnerability management. Athenisec will assess your application and system design to determine applicability and control mapping.
Implement Required Controls
Address identified gaps by implementing or updating security controls. This might include strengthening encryption, improving network segmentation, enhancing access management, or updating policies and procedures. Athenisec engineers develop best-practices to meet these requirements with the lowest impact on your organization.
Self-Assessment or External Audit
Depending on your merchant level, you'll either complete a Self-Assessment Questionnaire (SAQ) or undergo a formal audit by a Qualified Security Assessor (QSA). The QSA reviews your systems, tests controls, and verifies compliance with PCI DSS 4.0 requirements.
Submit Documentation and Attestation
After the audit or self-assessment, submit the necessary documentation, including the Report on Compliance (ROC) or SAQ, along with an Attestation of Compliance (AOC) to your clients or payment partners.
Maintenance
PCI DSS 4.0 emphasizes continuous compliance. Regularly monitor your systems, perform vulnerability scans, and ensure ongoing staff training to maintain compliance and prepare for annual re-assessments.
Highlights of PCI Compliance
The controls we implement and monitor throughout your PCI DSS engagement.
See how we’ve helped companies achieve and maintain compliance.
MediSync Health
Telemedicine SaaS platform connecting rural clinics with specialist doctors. 45-person team, $2.3M ARR.
- HIPAA
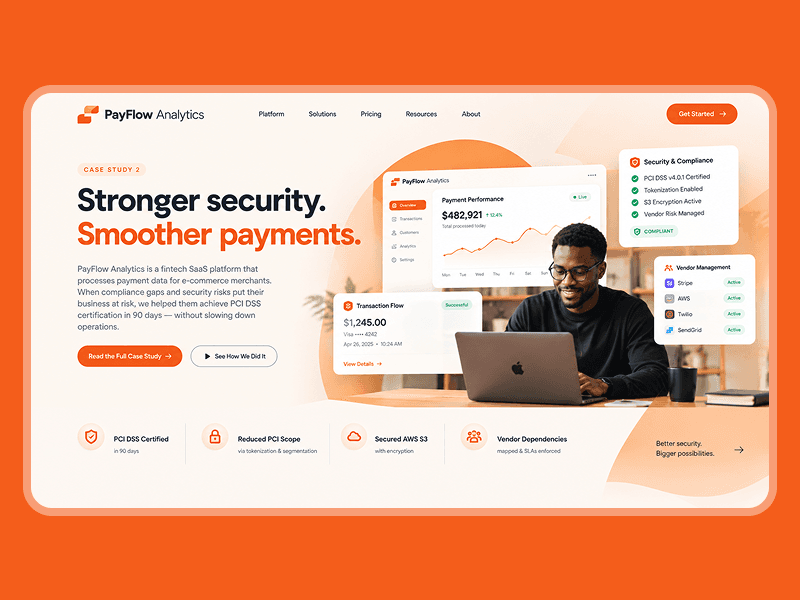
PayFlow Analytics
Fintech SaaS processing payment data for e-commerce merchants. 30-person team, $1.8M ARR.
- PCI DSS
CloudStack Enterprise
B2B SaaS infrastructure platform selling to enterprises. 60-person team, $4.2M ARR.
- SOC 2
- ISO 27001
- GDPR