Achieve & Maintain HIPAA with Unmatched Ease
Your dedicated team takes care of your entire HIPAA process from start to finish with uncompromising quality and speed.
Get StartedCertification Process Details
Planning
HIPAA sets standards for protecting Protected Health Information (PHI). Key components include the Privacy Rule, Security Rule, and Breach Notification Rule, which cover how PHI should be accessed, stored, transmitted, and reported in case of a breach.
Conduct a Risk Assessment
Perform a comprehensive risk assessment to identify vulnerabilities in how PHI is handled within your organization. This assessment is a critical first step in developing a compliant security framework.
Implement Safeguards and Policies
Based on the risk assessment, implement necessary administrative, physical, and technical safeguards. These may include access controls, encryption, incident response plans, and employee training on HIPAA policies.
Develop a HIPAA Compliance Program
Create and document a compliance program tailored to your organization's needs. This includes defining procedures for handling PHI, managing third-party business associate agreements (BAAs), and preparing for potential breaches.
Ensure Ongoing Compliance
HIPAA compliance is an ongoing process. Regularly update your risk assessments, retrain staff, and monitor your systems for potential vulnerabilities to maintain compliance and adapt to changes in regulations.
Highlights of HIPAA Compliance
The areas that make HIPAA compliance hardest to get right on your own.
See how we’ve helped companies achieve and maintain compliance.
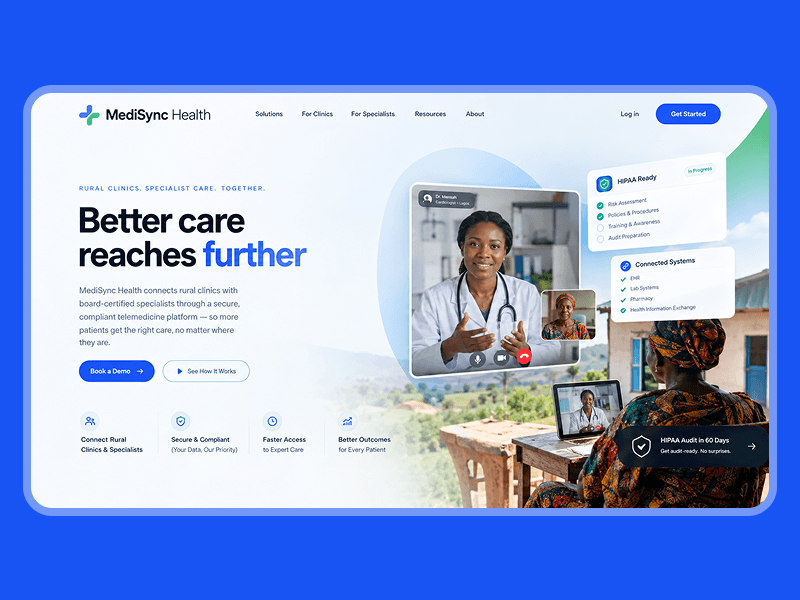
MediSync Health
Telemedicine SaaS platform connecting rural clinics with specialist doctors. 45-person team, $2.3M ARR.
- HIPAA
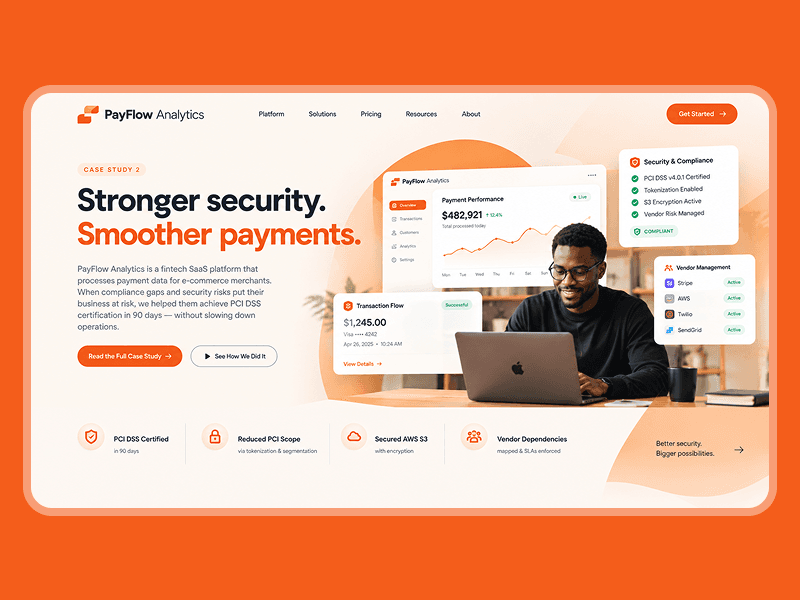
PayFlow Analytics
Fintech SaaS processing payment data for e-commerce merchants. 30-person team, $1.8M ARR.
- PCI DSS
CloudStack Enterprise
B2B SaaS infrastructure platform selling to enterprises. 60-person team, $4.2M ARR.
- SOC 2
- ISO 27001
- GDPR